
The Acorn application guide
Device Manager
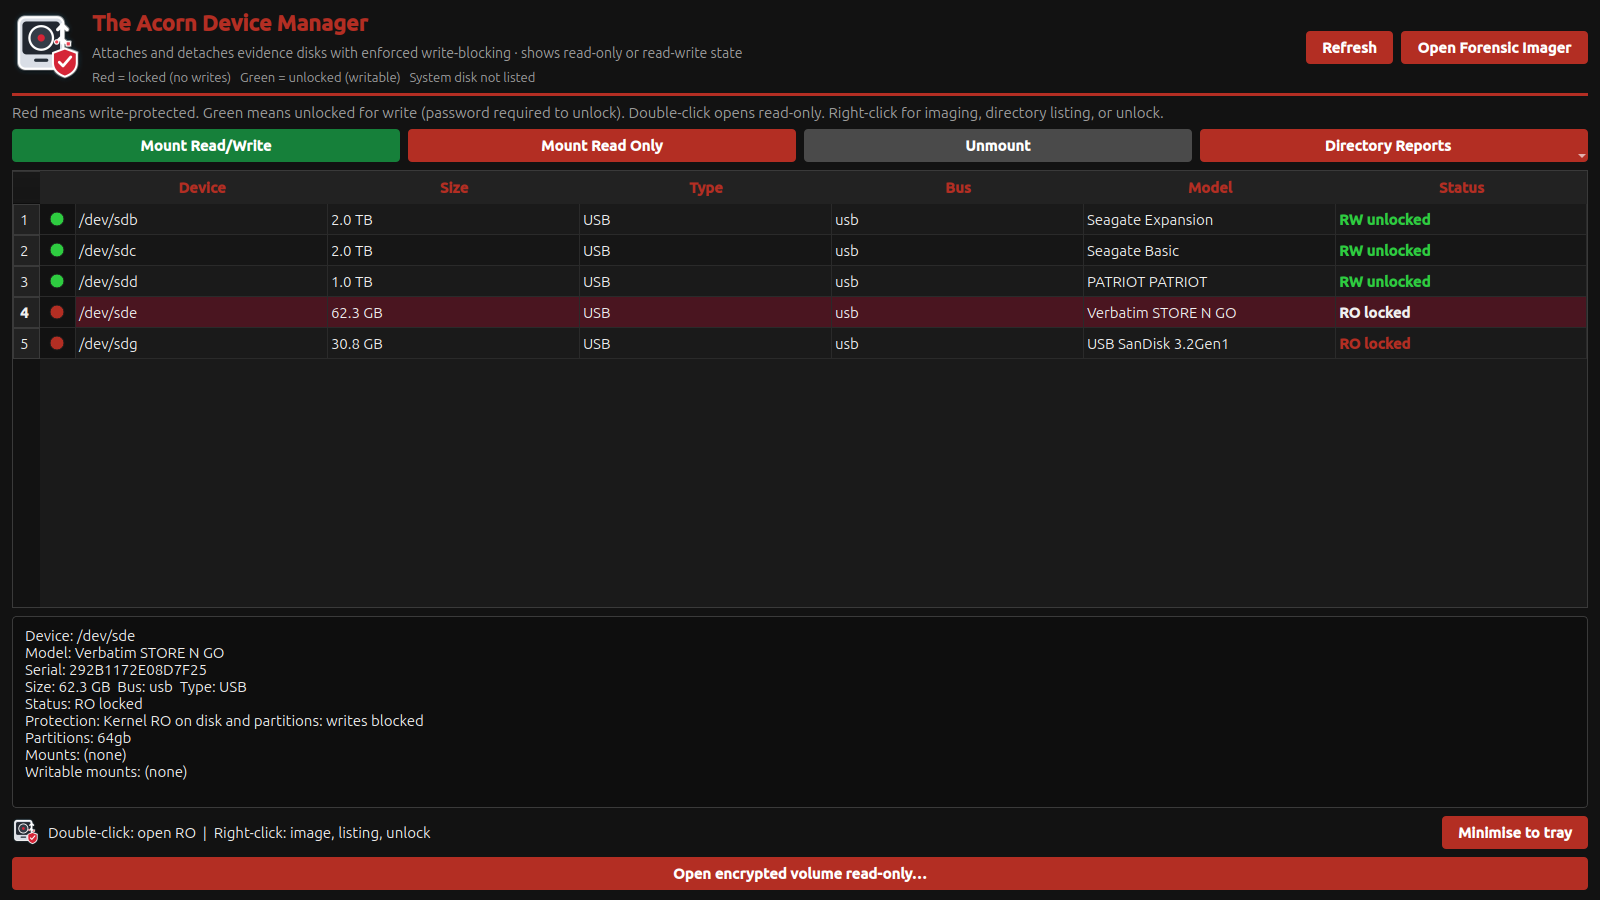
Check the connected device, its partitions and any mounts before choosing an action. The selected USB device is reported as read-only. That state is useful context, not independent proof that every write attempt would be blocked.
Native device-state inspection
Identify a device and inspect its protection state
Example input
- Connected-device and partition information displayed by the operating system.
Result or controls shown
- Device, partition, mount and protection-state information for examiner review.
 View full screen
Enlarge the screenshot to read the source records.
Examination steps
Steps to review in your evaluation
-
Match the intended source to the displayed device and partition details. Keep the evidence source separate from storage used for working outputs.
-
Inspect the reported read-only and mount states before selecting an access route. Record the observation and the protection method being relied upon.
-
Where protection is material to the task, check it using an appropriate controlled method and test media. Recheck the reported state after any deliberate change to the connection or workflow.
Evaluate the workflow
Questions worth bringing to a demonstration
- Can I identify the intended source unambiguously from the displayed device and partition information?
- What is an observed operating-system state, and what has actually been tested about the protection method?
- For my intended hardware and access route, which controlled checks should be completed before handling evidence?
Related application guides
Start with your requirements
Request an application demo
Tell us the source type and task you want to examine. We can plan a demo using suitable training material. Do not send confidential evidence.